Navigation indicator

Every Update, Double-Checked: Introducing Visual Checks for WordPress Care

October 9, 2026
Updates keep your site safe. Occasionally, they also break it.

Every WordPress site runs on WordPress itself, a theme and a collection of plugins. Each one gets regular updates that fix security holes, squash bugs and keep everything compatible. Skipping them isn’t an option.

But every so often, an update changes something it shouldn’t. A section shifts out of place. A button disappears on phones. A contact form quietly stops sending. Too often, the first person to notice is a customer.

That’s why Varial Hosting’s WordPress Care plan has always tested every update on a private staging copy before it reaches your live site. Now we’ve added a new layer to that process: automated visual checks, using a tool we built in-house, that compare your site before and after every update.

Why “it looks fine” isn’t enough

The problems updates cause are rarely dramatic. They’re small and easy to miss:

  • A layout change that only appears on mobile
  • A page halfway down your menu that nobody thought to check
  • A script error that breaks a form or menu without changing how the page looks

Checking every important page, at every screen size, by eye alone is slow. And after the twentieth page, even a careful person starts to skim.

How we update your site now

Each week, your updates start on a private staging copy of your site, never on the live version. Here’s what happens:

  1. Before screenshots. Our tool captures full-page screenshots of your key pages, at both desktop and mobile sizes.
  2. Updates on staging. We update WordPress, your theme and your plugins on the staging copy.
  3. After screenshots. The tool captures the same pages again, the same way.
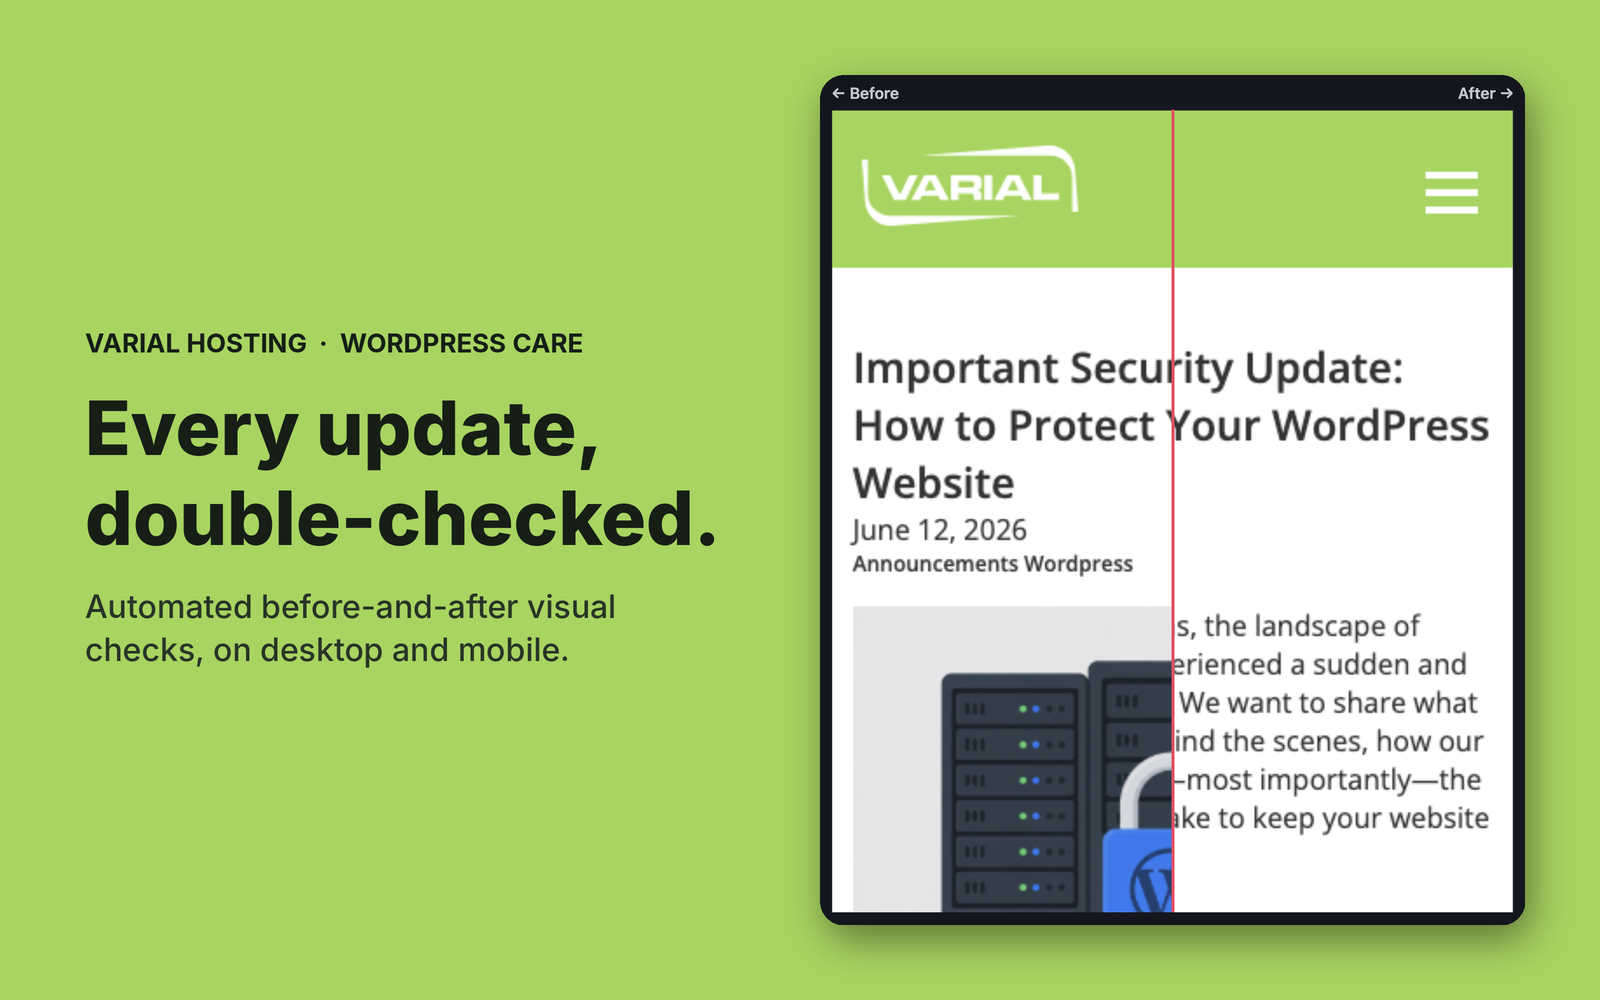
  4. Automatic comparison. Every page is compared pixel by pixel, and anything that changed is highlighted in red.
  5. Human review. We personally review every page the tool flags, side by side.
  6. Live update. Only once everything checks out do we back up your live site and apply the same updates.

We built this tool ourselves, specifically for the WordPress sites we look after. It runs on our own systems, so your screenshots and staging site details stay with us instead of being sent to a third-party service. And because it’s ours, we keep refining it as we learn how real WordPress sites behave.

The tool doesn’t replace our judgment. It points it at exactly the right places.

What the visual check catches

  • Layout changes: shifted sections, overlapping text, missing images or changed fonts, highlighted so we see exactly where.
  • Mobile-only problems: every page is checked at phone width too, where many update issues first appear.
  • Pages that stop working: a page that suddenly returns an error or fails to load.
  • Hidden errors: new JavaScript errors or missing files that can break forms, menus or checkout, even when the page looks identical.

What this means for you

  • Problems get caught on staging, before your visitors or customers ever see them.
  • Fewer surprises after update day, on desktop and mobile alike.
  • A visual record of your site. We keep screenshots from recent update cycles, so if something changes, we can see what it looked like before and when it changed.

You don’t need to do anything differently. Your site simply gets a more thorough check every time it’s updated.

Peace of mind, built in

Visual checks are now part of every Varial Hosting WordPress Care plan. If you’re already a Care client, they’re running on your site from your next weekly update.

Not a Care client yet? WordPress Care is $49/month per site, with no contracts. It also includes 24/7 monitoring, managed PHP upgrades and 30 minutes of webmaster help every month. Learn more about WordPress Care or contact us, and we’ll keep your WordPress site updated, secure and looking exactly the way it should.
PHP 8.5 Now Available

August 13, 2026

PHP 8.5 is now available to all Varial Hosting customers.

PHP 8.5 builds upon the great improvements brought forward in previous PHP 8 releases, and introduces several new features for developers which you can read about at: https://www.php.net/manual/en/migration85.php

To change your PHP version, simply log into your cPanel and follow this guide:
https://my.varialhosting.com/knowledgebase/98/How-do-I-change-PHP-versions.html

Please be aware that not all web applications and PHP extensions are compatible with PHP 8.5 at this time. For best compatibility we recommend using PHP 8.4 until development of PHP 8.5 matures.

Critical WordPress Core Vulnerability (wp2shell) – What You Need to Know

July 20, 2026

On July 17th, the WordPress Security Team released urgent patches for wp2shell, considered the worst security vulnerability in the WordPress core in nearly a decade.

Because this vulnerability exists in the WordPress application core—affecting hundreds of millions of sites across the global internet—we want to outline what took place, explain its impact and share the immediate steps we took across our infrastructure to keep your sites safe.

What Makes wp2shell So Serious?

  • Widespread Global Impact: This is a software vulnerability within the WordPress core codebase affecting hundreds of millions of websites worldwide.
  • No Extras Required: Unlike most security issues that target specific plugins or themes, this vulnerability exists directly in the main WordPress core software. It requires no plugins, no themes or even logged-in access to exploit.
  • Affected Versions: The vulnerability impacts WordPress core release branches 6.8, 6.9 and 7.0.
  • Immediate Threat: Automated exploit attempts began targeting vulnerable sites globally within hours of public disclosure on July 17th.

Actions We Have Already Taken

To protect client websites and maintain environment integrity, our team took immediate action upon the official patch release on July 17th:

  1. WordPress Care & Maintenance Subscribers: All client websites subscribed to our WordPress Care & Maintenance plan were audited and updated immediately.
  2. Installatron Automatic Updates: Sites configured with automatic core updates enabled in Installatron were automatically patched to safe versions that night.
  3. Web Application Firewall Protection: We deployed server-level firewall rules across our platform to intercept and block known exploit attempts.

What You Need to Do

While our active firewall rules block incoming attack attempts, updating your WordPress software to a patched release is the only permanent fix.

  • If your WordPress site is already updated to version 6.8.6, 6.9.5 or 7.0.2 (or higher):
    You are fully protected! No further action is required.
  • If your site is running a vulnerable version of the 6.8, 6.9 or 7.0 branch:
    Please update your site immediately. You can do this easily in one of two ways:
    • Option 1: Log in to your cPanel control panel, open Installatron, locate your WordPress site and click the update button.
    • Option 2: Log in directly to your WordPress Admin Dashboard (/wp-admin), navigate to Dashboard > Updates, and click Update Now.

If you have any questions or need assistance verifying whether your site is running a safe version, please open a support ticket with our technical support team—we are here to help!

Scheduled Maintenance: MariaDB Database Upgrades [Completed]

June 18, 2026

Varial Hosting Scheduled Maintenance

In the evening of Friday, June 26, 2026, we will be performing a major database engine upgrade on our Chang, Diggory, Flitwick, Lovegood and Tonks servers. The database software will be updated from MariaDB 10.6 to MariaDB 10.11 (LTS).

This upgrade ensures your applications continue to run on a highly secure, optimized and long-term supported database environment.

What to Expect:

  • Downtime: Websites utilizing MariaDB/MySQL databases on these specific servers will be temporarily unavailable for approximately 10 to 15 minutes while the upgrade process finishes.
  • Impact: Visitors accessing database-driven websites during this short window may encounter a database connection error. Static pages that do not use a database will remain fully functional.

Technical Notes & Changes:

MariaDB 10.11 is a major Long-Term Support release that introduces performance optimizations, advanced features like dynamic InnoDB variables and enhanced query optimizer telemetry.

While the upgrade is designed to be fully backward-compatible for standard website architectures (such as WordPress), advanced developers can review the official MariaDB 10.6 to 10.11 Upgrade Guide for a comprehensive breakdown of changed parameter defaults and performance adjustments.

We appreciate your patience and understanding as we work to improve our hosting infrastructure. If you have any questions or experience unexpected issues following the window, please open a ticket with our support team.

Important Security Update: How to Protect Your WordPress Website

June 12, 2026

Over the past few months, the landscape of website security has experienced a sudden and dramatic paradigm shift. We want to share what we have been facing behind the scenes, how our industry is evolving and—most importantly—the practical steps you can take to keep your website safe.

The New Reality: AI-Accelerated Exploits

Historically, website security operated at a predictable pace. A critical vulnerability might surface once or twice a year, giving website owners and system administrators plenty of time to review change logs, assess threats and schedule a convenient patch window.

That era is officially over.

As detailed in our recent blog post, Securing Your Websites Against 0-Day Threats, we have faced a rapid, continuous barrage of critical zero-day threats occurring weekly, and at times even daily.

This shift is being driven by the maturation of advanced AI tools. Both security researchers and malicious actors are now using AI to audit source code at lightning speed.

  • The Good: Defenders can find deep, systemic flaws that went unnoticed by human eyes for years.
  • The Bad: The moment a patch or a public disclosure is released, automated tools can instantly reverse-engineer it to find the exploit.

As a result, vulnerabilities are being actively exploited in the wild mere hours after public disclosure. The traditional concept of “scheduling a patch window next week” is no longer viable. Maintaining security now requires constant, immediate attention.

Looking Ahead: The Next 3 to 12 Months

Our security vendors have declared that we are in the middle of a permanent industry shift. Experts project that this rapid pace of vulnerability discoveries will persist aggressively for the next 3 to 6 months, with an elevated threat environment remaining for the next 1 to 2 years as AI tools continue to improve.

Continuous, automated updating is the new standard for web safety.

Why Keeping Your WordPress Software Current Matters

Because the vast majority of our customers run on WordPress, it’s vital to understand how this impacts your daily operations.

The #1 cause of website compromises is failing to keep website software up to date.

WordPress plugins are highly targeted by attackers using AI tools to find hidden flaws. A prime example occurred recently with UpdraftPlus, a massive backup plugin with millions of installations. A critical vulnerability was discovered that allowed for full website compromise if left unpatched.

When your site runs outdated plugins, it is only a matter of time before automated scripts locate the vulnerability.

Server-Level Defence vs. Core Patching

To help counter these threats, all Varial Hosting plans include an AI-driven, proactive firewall designed to help intercept malicious traffic and mitigate many zero-day exploits in real time. Powered by our Imunify360 security suite, its malware protection also adds an extra layer of defence by working to automatically detect and quarantine known malicious code before it can cause damage to your site.

While these server-level features are must-have modern security tools, patching vulnerable application code directly remains the single best defence against exploits.

3 Ways to Keep Your WordPress Site Up to Date

To protect your business and reputation, you need an update strategy that fits your workflow. We provide three distinct paths to handle this on our platform:

1. Manual Updates via WP-Admin (Self-Managed)

You can log directly into your WordPress wp-admin dashboard regularly to manually update your WordPress core, plugins and themes. Because of the accelerated timeline of modern attacks, you should frequently check for and apply updates to ensure you aren’t left exposed to active exploits.

2. Automated or Manual Updates via Installatron in cPanel (Recommended)

You can utilize the Installatron tool located inside your cPanel control panel. Installatron offers a massive safety net: it automatically takes a complete backup of your website before performing any update, allowing you to easily roll back with a single click if there are any issues.

  • WordPress Core (Our Default): By default, Installatron is set to automatically update your core WordPress software. Core releases are heavily tested and rarely introduce bugs.
  • Plugins and Themes (Optional): Automatic updates for plugins and themes are optional and turned off by default. Because anyone can write a plugin, they may not be as thoroughly tested and could occasionally introduce conflicts or functionality changes that could negatively impact your website. If you choose to enable automatic updates for plugins and themes, we highly recommend reviewing your website after receiving an update notification to ensure everything is working properly.

3. WordPress Care & Maintenance Plan (Fully Managed)

For businesses and organizations that want total peace of mind without the hassle, our fully managed WordPress Care & Maintenance Plan is available.

With this plan, our team handles the entire process for you. We don’t just blindly update your site; we deploy and test all updates in a private staging environment first to ensure there are no conflicts or layout issues before safely pushing them live. This allows you to focus 100% on running your business while we ensure your website remains locked down.

The security landscape has changed permanently, but by shifting to a proactive, continuous update mindset, you can keep your data and websites secure.

If you would like to enrol in our Care & Maintenance plan, or need help configuring Installatron for automated backups and updates, please contact us or open a ticket with our support team.