Navigation indicator

Security Update: All PHP versions patched against recent PHP vulnerabilities

October 21, 2026

Varial Hosting PHP Security

All PHP versions on our servers have been patched against the two critical security vulnerabilities disclosed today, CVE-2026-109618 and CVE-2026-109619.

Here is a brief summary of what happened and how we secured your hosting environment:

What Happened

PHP is the programming language that powers over 70% of the web, including popular applications like WordPress, Joomla, and Drupal. On October 20th, preliminary details of critical security vulnerabilities leaked ahead of schedule, prompting a rush by security researchers and bad actors to locate the flaw before fixed versions could be published. A proof-of-concept exploit tool named php2shell surfaced shortly after, demonstrating potential remote compromises of vulnerable PHP applications.

How We Protected Your Site

Our team worked continuously to monitor the situation and apply multiple layers of defense:

  • Preemptive Protection: Out of an abundance of caution, we temporarily took down our main website (varialhosting.com) and client portal on October 20th to display a maintenance page to protect customer data.
  • Immediate Mitigations: We applied protective PHP configuration changes across our servers and updated our Web Application Firewall (WAF) rules to block exploit patterns and scanning activity.
  • Backported Security Patches: To minimize the chance of unexpected complications or plugin incompatibilities that can occur with full version upgrades during an emergency, our security partner applied security patches directly to the PHP releases currently running on our servers (covering PHP 5.2 through 8.5). This ensures your environment receives the necessary protection without requiring a PHP version bump.

Current Status

  • All PHP Versions Patched: Every PHP version offered on our servers is protected against CVE-2026-109618 and CVE-2026-109619.
  • Services Fully Restored: Our website and client area are back online and functioning normally.
  • No Compromises Detected: We have observed no signs of security breaches on our network, a status confirmed by other hosting providers using our security partner’s protections.

Thank you for your patience while our team worked to safeguard your websites. If you have any questions, please feel free to reach out to our support team.

Every Update, Double-Checked: Introducing Visual Checks for WordPress Care

October 9, 2026

Updates keep your site safe. Occasionally, they also break it.

Every WordPress site runs on WordPress itself, a theme and a collection of plugins. Each one gets regular updates that fix security holes, squash bugs and keep everything compatible. Skipping them isn’t an option.

But every so often, an update changes something it shouldn’t. A section shifts out of place. A button disappears on phones. A contact form quietly stops sending. Too often, the first person to notice is a customer.

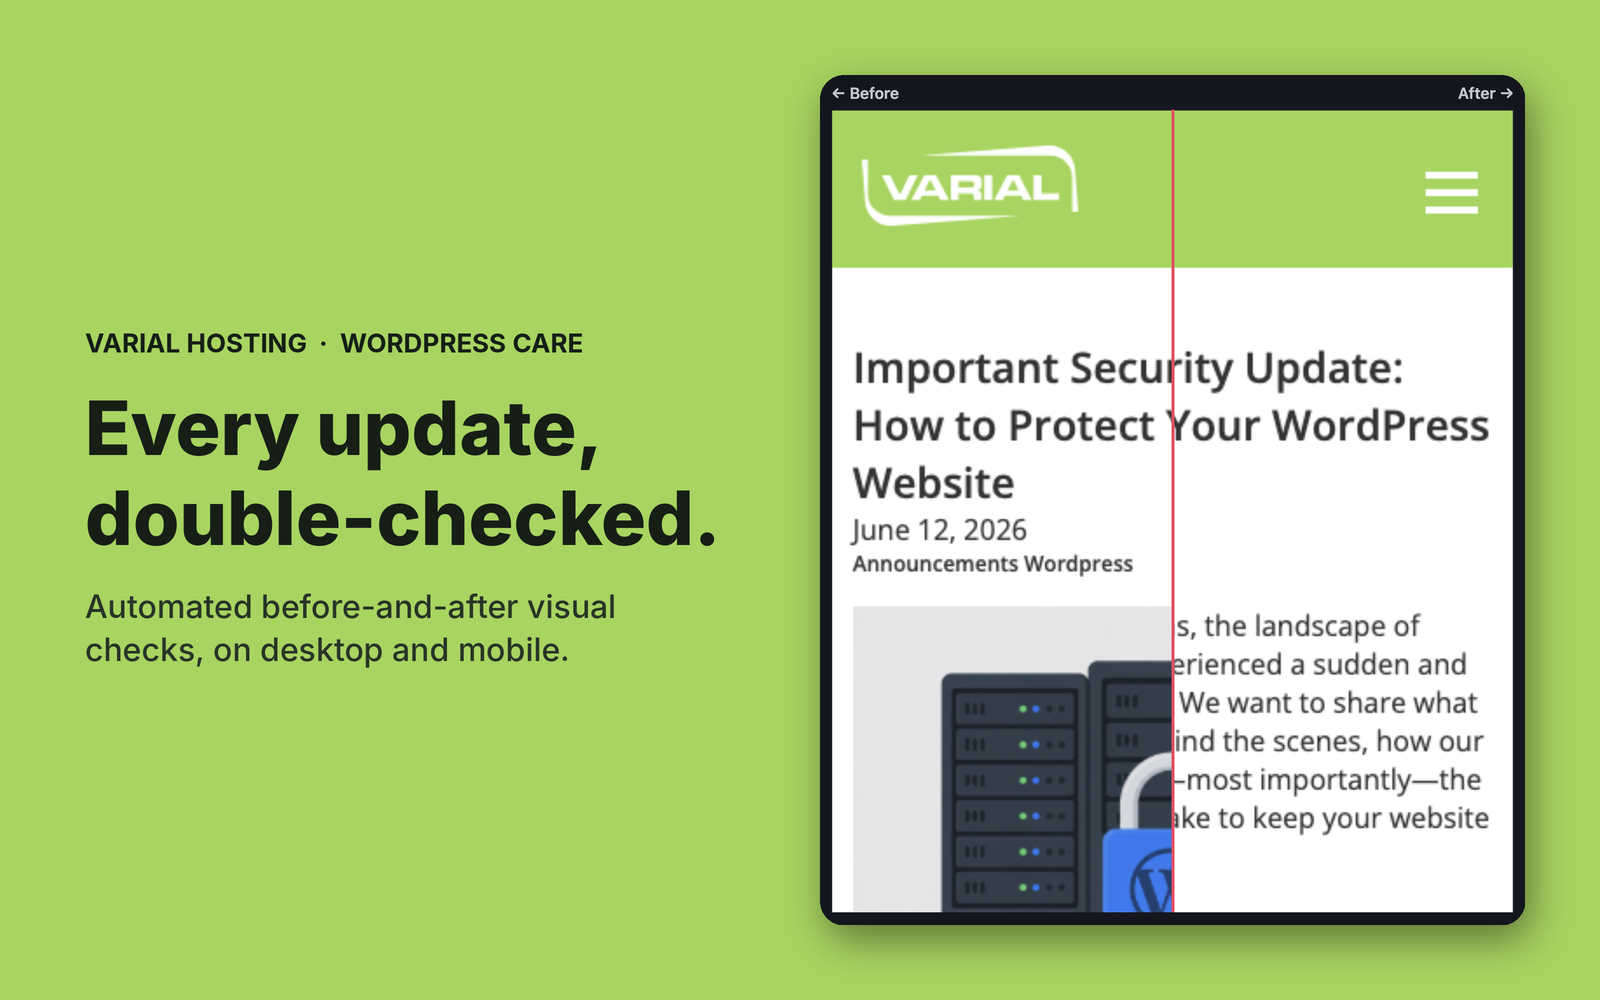
That’s why Varial Hosting’s WordPress Care plan has always tested every update on a private staging copy before it reaches your live site. Now we’ve added a new layer to that process: automated visual checks, using a tool we built in-house, that compare your site before and after every update.

Why “it looks fine” isn’t enough

The problems updates cause are rarely dramatic. They’re small and easy to miss:

  • A layout change that only appears on mobile
  • A page halfway down your menu that nobody thought to check
  • A script error that breaks a form or menu without changing how the page looks

Checking every important page, at every screen size, by eye alone is slow. And after the twentieth page, even a careful person starts to skim.

How we update your site now

Each week, your updates start on a private staging copy of your site, never on the live version. Here’s what happens:

  1. Before screenshots. Our tool captures full-page screenshots of your key pages, at both desktop and mobile sizes.
  2. Updates on staging. We update WordPress, your theme and your plugins on the staging copy.
  3. After screenshots. The tool captures the same pages again, the same way.
  4. Automatic comparison. Every page is compared pixel by pixel, and anything that changed is highlighted in red.
  5. Human review. We personally review every page the tool flags, side by side.
  6. Live update. Only once everything checks out do we back up your live site and apply the same updates.

We built this tool ourselves, specifically for the WordPress sites we look after. It runs on our own systems, so your screenshots and staging site details stay with us instead of being sent to a third-party service. And because it’s ours, we keep refining it as we learn how real WordPress sites behave.

The tool doesn’t replace our judgment. It points it at exactly the right places.

What the visual check catches

  • Layout changes: shifted sections, overlapping text, missing images or changed fonts, highlighted so we see exactly where.
  • Mobile-only problems: every page is checked at phone width too, where many update issues first appear.
  • Pages that stop working: a page that suddenly returns an error or fails to load.
  • Hidden errors: new JavaScript errors or missing files that can break forms, menus or checkout, even when the page looks identical.

What this means for you

  • Problems get caught on staging, before your visitors or customers ever see them.
  • Fewer surprises after update day, on desktop and mobile alike.
  • A visual record of your site. We keep screenshots from recent update cycles, so if something changes, we can see what it looked like before and when it changed.

You don’t need to do anything differently. Your site simply gets a more thorough check every time it’s updated.

Peace of mind, built in

Visual checks are now part of every Varial Hosting WordPress Care plan. If you’re already a Care client, they’re running on your site from your next weekly update.

Not a Care client yet? WordPress Care is $49/month per site, with no contracts. It also includes 24/7 monitoring, managed PHP upgrades and 30 minutes of webmaster help every month. Learn more about WordPress Care or contact us, and we’ll keep your WordPress site updated, secure and looking exactly the way it should.

Important Security Update: How to Protect Your WordPress Website

June 12, 2026

Over the past few months, the landscape of website security has experienced a sudden and dramatic paradigm shift. We want to share what we have been facing behind the scenes, how our industry is evolving and—most importantly—the practical steps you can take to keep your website safe.

The New Reality: AI-Accelerated Exploits

Historically, website security operated at a predictable pace. A critical vulnerability might surface once or twice a year, giving website owners and system administrators plenty of time to review change logs, assess threats and schedule a convenient patch window.

That era is officially over.

As detailed in our recent blog post, Securing Your Websites Against 0-Day Threats, we have faced a rapid, continuous barrage of critical zero-day threats occurring weekly, and at times even daily.

This shift is being driven by the maturation of advanced AI tools. Both security researchers and malicious actors are now using AI to audit source code at lightning speed.

  • The Good: Defenders can find deep, systemic flaws that went unnoticed by human eyes for years.
  • The Bad: The moment a patch or a public disclosure is released, automated tools can instantly reverse-engineer it to find the exploit.

As a result, vulnerabilities are being actively exploited in the wild mere hours after public disclosure. The traditional concept of “scheduling a patch window next week” is no longer viable. Maintaining security now requires constant, immediate attention.

Looking Ahead: The Next 3 to 12 Months

Our security vendors have declared that we are in the middle of a permanent industry shift. Experts project that this rapid pace of vulnerability discoveries will persist aggressively for the next 3 to 6 months, with an elevated threat environment remaining for the next 1 to 2 years as AI tools continue to improve.

Continuous, automated updating is the new standard for web safety.

Why Keeping Your WordPress Software Current Matters

Because the vast majority of our customers run on WordPress, it’s vital to understand how this impacts your daily operations.

The #1 cause of website compromises is failing to keep website software up to date.

WordPress plugins are highly targeted by attackers using AI tools to find hidden flaws. A prime example occurred recently with UpdraftPlus, a massive backup plugin with millions of installations. A critical vulnerability was discovered that allowed for full website compromise if left unpatched.

When your site runs outdated plugins, it is only a matter of time before automated scripts locate the vulnerability.

Server-Level Defence vs. Core Patching

To help counter these threats, all Varial Hosting plans include an AI-driven, proactive firewall designed to help intercept malicious traffic and mitigate many zero-day exploits in real time. Powered by our Imunify360 security suite, its malware protection also adds an extra layer of defence by working to automatically detect and quarantine known malicious code before it can cause damage to your site.

While these server-level features are must-have modern security tools, patching vulnerable application code directly remains the single best defence against exploits.

3 Ways to Keep Your WordPress Site Up to Date

To protect your business and reputation, you need an update strategy that fits your workflow. We provide three distinct paths to handle this on our platform:

1. Manual Updates via WP-Admin (Self-Managed)

You can log directly into your WordPress wp-admin dashboard regularly to manually update your WordPress core, plugins and themes. Because of the accelerated timeline of modern attacks, you should frequently check for and apply updates to ensure you aren’t left exposed to active exploits.

2. Automated or Manual Updates via Installatron in cPanel (Recommended)

You can utilize the Installatron tool located inside your cPanel control panel. Installatron offers a massive safety net: it automatically takes a complete backup of your website before performing any update, allowing you to easily roll back with a single click if there are any issues.

  • WordPress Core (Our Default): By default, Installatron is set to automatically update your core WordPress software. Core releases are heavily tested and rarely introduce bugs.
  • Plugins and Themes (Optional): Automatic updates for plugins and themes are optional and turned off by default. Because anyone can write a plugin, they may not be as thoroughly tested and could occasionally introduce conflicts or functionality changes that could negatively impact your website. If you choose to enable automatic updates for plugins and themes, we highly recommend reviewing your website after receiving an update notification to ensure everything is working properly.

3. WordPress Care & Maintenance Plan (Fully Managed)

For businesses and organizations that want total peace of mind without the hassle, our fully managed WordPress Care & Maintenance Plan is available.

With this plan, our team handles the entire process for you. We don’t just blindly update your site; we deploy and test all updates in a private staging environment first to ensure there are no conflicts or layout issues before safely pushing them live. This allows you to focus 100% on running your business while we ensure your website remains locked down.

The security landscape has changed permanently, but by shifting to a proactive, continuous update mindset, you can keep your data and websites secure.

If you would like to enrol in our Care & Maintenance plan, or need help configuring Installatron for automated backups and updates, please contact us or open a ticket with our support team.

cPanel Upgraded to v134 Across All Servers

May 5, 2026

cPanel Logo

We are excited to announce that all Varial Hosting servers have been upgraded to the latest version of cPanel (v134). This update brings several new tools to help you manage your website and email more easily.

Here are the most helpful changes for you:

Easier Website Testing & Management

  • Temporary Domain Names: Ever wanted to start building your website before your domain name was officially registered or moved to us? You can now create a temporary domain to preview and test your site during development.
  • Simplified Security: We’ve combined several security pages into one Unified SSL/TLS interface. This makes it much easier to see if your website’s “padlock” icon is active and up to date.
  • Centralized Settings: You can now manage your account password, contact info and language preferences from one single location in cPanel, saving you from clicking through multiple menus.

Better Email Experience

  • Webmail Filtering: You can now create and manage email filters (rules that automatically move or delete certain emails) directly inside Webmail. You no longer need to log into the main cPanel dashboard to organize your inbox.
  • Enhanced Mail Security: We’ve upgraded our mail server software to improve performance. For your protection, this version requires stronger password security. If you haven’t changed your email password in many years, you may be prompted to update it to a more secure one.

Behind-the-Scenes Improvements

  • Faster Performance: With upgrades to Perl and better support for modern operating systems, your hosting environment is now faster, more stable and better equipped to run the latest web applications.

Securing Your Websites Against 0-Day Threats: How Varial Hosting Responded to This Week’s Critical Security Vulnerabilities

May 1, 2026

Securing Your Websites Against 0-Day Threats

TLDR; Our servers are fully patched against this week’s high-profile cPanel (CVE-2026-41940) and “Copy Fail” Linux (CVE-2026-31431) security threats. No action is required on your part; our team has already handled these updates for you.

This week was a busy one for our security team.

Rapid Response to the cPanel Authentication Vulnerability

On Tuesday, April 28th, a critical vulnerability was identified in cPanel (CVE-2026-41940). This flaw was particularly serious because it allowed for an “authentication bypass”—essentially meaning an attacker could gain administrative access to a server without needing a password.

Because we stay active in core industry security circles, we were alerted to this risk early. Following best practices, we took the proactive step of temporarily restricting access to cPanel, WHM and Webmail. This “closed the door” while we waited for the official software patch to be finalized.

Once the patch was released that afternoon, our team tested and deployed it across our entire network immediately—finishing the work many hours before standard nightly maintenance would have even begun.

By the time cPanel’s official email alert reached most server owners the following day, the digital landscape was already seeing a massive spike in exploit attempts. We are pleased to report that because of our team’s early intervention, Varial Hosting servers were fully secured before these global attacks even began.

Protecting Server Integrity Against the “Copy Fail” Threat

The very next day, Wednesday, April 29th, a second global threat emerged.

A vulnerability nicknamed “Copy Fail” (CVE-2026-31431) was discovered, affecting almost all Linux-based systems worldwide. This flaw could allow a low-level user to “escalate” their permissions to gain total control of a server.

Because the primary risk involved secure shell (SSH) access, we took the immediate precaution of temporarily disabling customer SSH and implementing early defenses while waiting for an official fix from our OS vendors.

When it became clear that a final patch would take some time to arrive, we decided not to wait. We implemented a “kernel-level” mitigation—a deep-system fix that required a full server reboot to activate.

Prioritizing Security Over Uptime

While we take pride in our ability to perform “rebootless” updates (some of our servers hadn’t needed a restart in over two years!), the emerging risk was too high to ignore. Security experts warned that hackers might try to use outdated or compromised WordPress sites as a “back door” to trigger this exploit. To ensure your data remained 100% isolated and secure, we performed a controlled reboot across our fleet last night.

As of this morning, we are happy to confirm that all servers are now running the fully patched kernel, and this vulnerability is closed.

Our Commitment to Your Security

At Varial Hosting, we know that you count on us to manage the complex world of server security so you don’t have to. While “0-day” threats like these make headlines, they are a routine part of our workday. Our team remains vigilant, monitoring global threat feeds 24/7 and testing patches before they are even officially announced to the general public.

We take these proactive steps to ensure that your business remains online and your data remains private, without you ever having to lift a finger.

Questions?

If you have any questions about these updates or our security protocols, our support team is always here to help. Feel free to open a support ticket or reach out to us directly.